South Africa’s proposed National Opt-Out Registry is intended to help consumers stop unwanted marketing calls, but concerns have emerged over whether the system could expose personal information to cybercriminals and increase compliance costs for businesses.
- Why the Proposed Spam Call Registry Is Raising Concerns
- The Privacy Paradox Behind the Registry
- An Alternative: Suppression Lists That Limit Data Exposure
- Monthly Fees Could Increase Marketing Costs
- Heavy Penalties for Businesses That Fail to Comply
- NCC Responds to Cybersecurity and Privacy Concerns
- What the Proposed Rules Could Mean for Ordinary South Africans
Ahmore Burger-Smidt, head of regulatory at Werksmans Attorneys, has warned that the draft guidelines could create significant privacy and cybersecurity risks if large volumes of consumer information are concentrated in a central database.
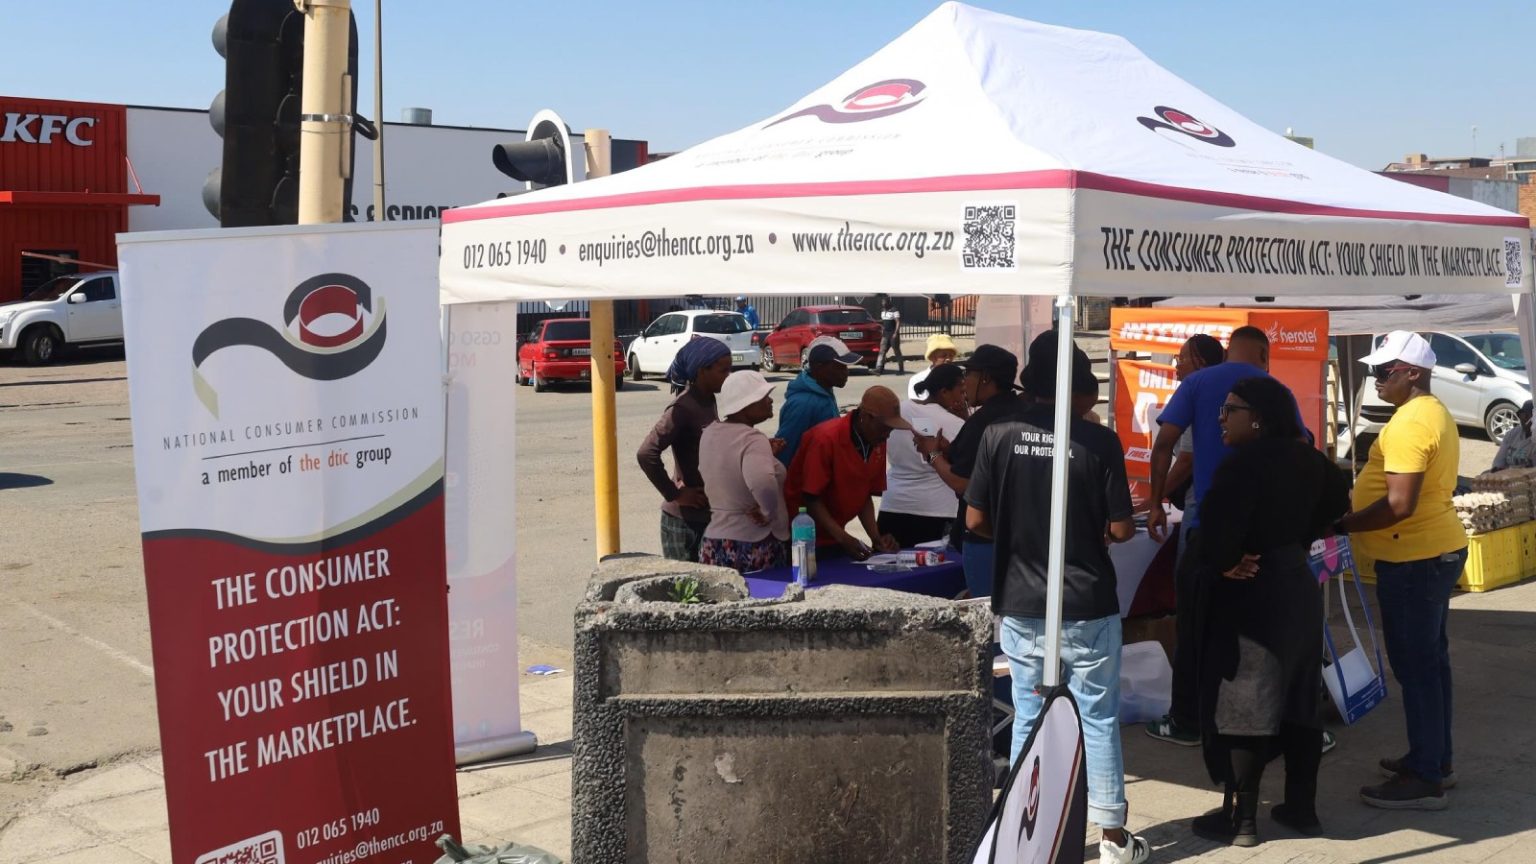
The National Consumer Commission (NCC), which is responsible for the initiative, maintains that protecting users’ information is a key consideration and says security controls have been incorporated into the system’s design.
The debate now centres on whether the proposed registry can protect South Africans from unwanted calls without creating new risks for their personal data or placing unnecessary burdens on businesses.
Why the Proposed Spam Call Registry Is Raising Concerns
Under the draft guidelines, direct marketers would be required to register before conducting direct marketing and renew their registration annually.
The proposed requirements cover businesses across multiple industries, including retailers, insurers, financial institutions, estate agencies, vehicle dealerships and digital marketers.
Burger-Smidt’s main concern is the proposed requirement for marketers to upload customer databases to a state-run platform every month.
Such databases can contain names, telephone numbers, contact details and other information used to identify and classify potential customers.
According to Burger-Smidt, concentrating millions of consumer records in one location could make the platform an attractive target for cybercriminals. If that information were exposed, criminals could potentially use it for targeted phishing attacks, impersonation and other social engineering scams.
She argued that the draft guidelines do not adequately explain the safeguards governing how the information would be accessed, stored, shared and destroyed.
The Privacy Paradox Behind the Registry
The proposed system is intended to give South Africans greater control over unwanted marketing. However, Burger-Smidt argues that requiring extensive personal information to be uploaded to a central platform could undermine that objective.
She described this as a privacy paradox: consumers seeking protection from unsolicited calls could face additional exposure of their personal information.
Burger-Smidt also referred to Constitutional Court judgments involving AmaBhungane Centre for Investigative Journalism NPC and Another v Minister of Justice, which addressed safeguards around the handling of personal information and surveillance-related powers.
Her argument is that similar attention should be given to the protection of consumer data held by the state.
The concern is not that a data breach has necessarily occurred, but that the draft guidelines should clearly establish the protections governing the proposed system before it is fully implemented.
An Alternative: Suppression Lists That Limit Data Exposure

Instead of requiring marketers to upload raw customer information to one central database, Burger-Smidt has proposed a privacy-preserving approach based on suppression lists.
A suppression list identifies people who must be excluded from marketing campaigns because they have opted out, unsubscribed or registered on a do-not-call system.
Under the model she advocates, marketers would download lists of identifiers that must be excluded from campaigns, with published security standards governing how the information is handled.
The proposal also refers to using cryptographic hashes — transformed representations of data that can be used for matching without routinely exchanging the original information in plain text.
Such methods can reduce unnecessary exposure of personal details. However, hashing is not automatically anonymous or risk-free: the level of protection depends on how the system is designed, including the identifiers used and the safeguards against attempts to reverse or match the data.
The central question is whether the registry can achieve its consumer-protection objective while minimising the amount of personal information that needs to be centrally collected.
Monthly Fees Could Increase Marketing Costs
Data privacy is not the only issue raised by the draft guidelines. Burger-Smidt has also questioned the proposed recurring fee of 12 cents for every contact matched against the registry.
The matching process identifies contacts that marketers must exclude from their campaigns.
Because businesses would need to repeat the process every 30 days, the fee could become a recurring operational expense, particularly for companies maintaining large customer databases.
The proposed system could also require businesses to devote additional resources to registration, annual renewals, monthly checks and the management of updated suppression lists.
Burger-Smidt warned that companies would need to ensure they were acting on current lists to avoid accidentally contacting people who had opted out.
The overall financial impact would depend on the number of contacts processed, the final rules and how the registry operates in practice.
Heavy Penalties for Businesses That Fail to Comply
The draft guidelines also outline substantial penalties for non-compliance.
According to the information provided, direct marketers could face an administrative fine of up to R1 million or 10% of their annual gross turnover for the preceding financial year.
In serious cases, criminal prosecution could also follow, with imprisonment of up to 12 months.
These potential consequences raise the stakes for businesses that conduct direct marketing. Companies would need to understand the final requirements and establish processes to ensure that people who opt out are excluded from future campaigns.
The proposed penalties also make clear why the details of the final rules, including compliance procedures and safeguards, matter to businesses across numerous sectors.
NCC Responds to Cybersecurity and Privacy Concerns
The National Consumer Commission has defended the registry’s security arrangements, saying that data protection and privacy have been central considerations in its design and development.
In its response to MyBroadband, the NCC said the system incorporates multiple layers of security controls and has been developed with the Protection of Personal Information Act (POPIA) and other applicable requirements in mind.
The commission also said penetration testing is conducted periodically in line with industry standards. These tests involve authorised cybersecurity professionals attempting to identify vulnerabilities in a system.
The NCC added that it maintains ongoing security monitoring and incident-response processes.
It acknowledged that no digital system can responsibly be described as completely immune to cyber threats, but said it was committed to responding to emerging risks and improving its security measures.
The commission’s response addresses the concern that the system could be vulnerable, although the information provided does not independently establish the effectiveness of its controls or resolve every question about how consumer data will be handled.
What the Proposed Rules Could Mean for Ordinary South Africans
For consumers, the registry is intended to provide a formal way to reduce unwanted direct marketing calls. Its effectiveness will depend on how well marketers comply with opt-out requests and how reliably the system operates.
For businesses, the proposed requirements could introduce additional administrative responsibilities, recurring matching costs and potentially significant penalties for breaches.
The unresolved issue is how to balance these objectives: protecting consumers from unwanted marketing, safeguarding their personal information and ensuring that compliance requirements are practical.
Burger-Smidt has urged South Africans to use the opportunity to comment on the draft guidelines, arguing that privacy protections should be clearly established before the system proceeds.
The NCC, meanwhile, says it is committed to maintaining security and complying with data-protection legislation.
Ultimately, the registry’s success will depend not only on whether it reduces spam calls, but also on whether it protects the very people it is designed to serve.